Rsyslog Template
Create a template for log receipt. Each log entry have topic which describes the origin of log message. Amazon cloudwatch logs destinations deploy in the primary account and are created with the required permissions in. Rsyslog uses port 514 for network connectivity, whether it's using tcp or udp. You must deploy the aws cloudformation template in the aws account where you intend to store your log data.
Rsyslog Template - Once you've uncommented the transport layer protocol and set a template, save your changes to the file. The centralized logging on aws solution contains the following components: Many devices, especially routers and firewalls, do not send rfc compliant syslog messages. There can be more than one topic assigned to log message. Clickup is the online solution to let your team get more done! Udp is also supported and the recommended way to send log messages in most architectures. Open /etc/rsyslog.conf with a text editor, and append the following template before the global directives block: Create a template for log receipt. Each log entry have topic which describes the origin of log message. In this step, we will configure our centralized rsyslog server to use a json template to format the log data before sending it to logstash, which will then send it to elasticsearch on a different server.
Rsyslog Template Gallery

Configure Rsyslog Centralized Log Server on Ubuntu 20.0418.04
随 rsyslog 版本不同,如果有如下警告信息,则将 ~ 修改为 stop。. Route, ospf, debug and raw. Easily manage your team's.

搭建rsyslog日志服务器 Bypass 博客园
Graylog is able to accept and parse rfc 5424 and rfc 3164 compliant syslog messages.
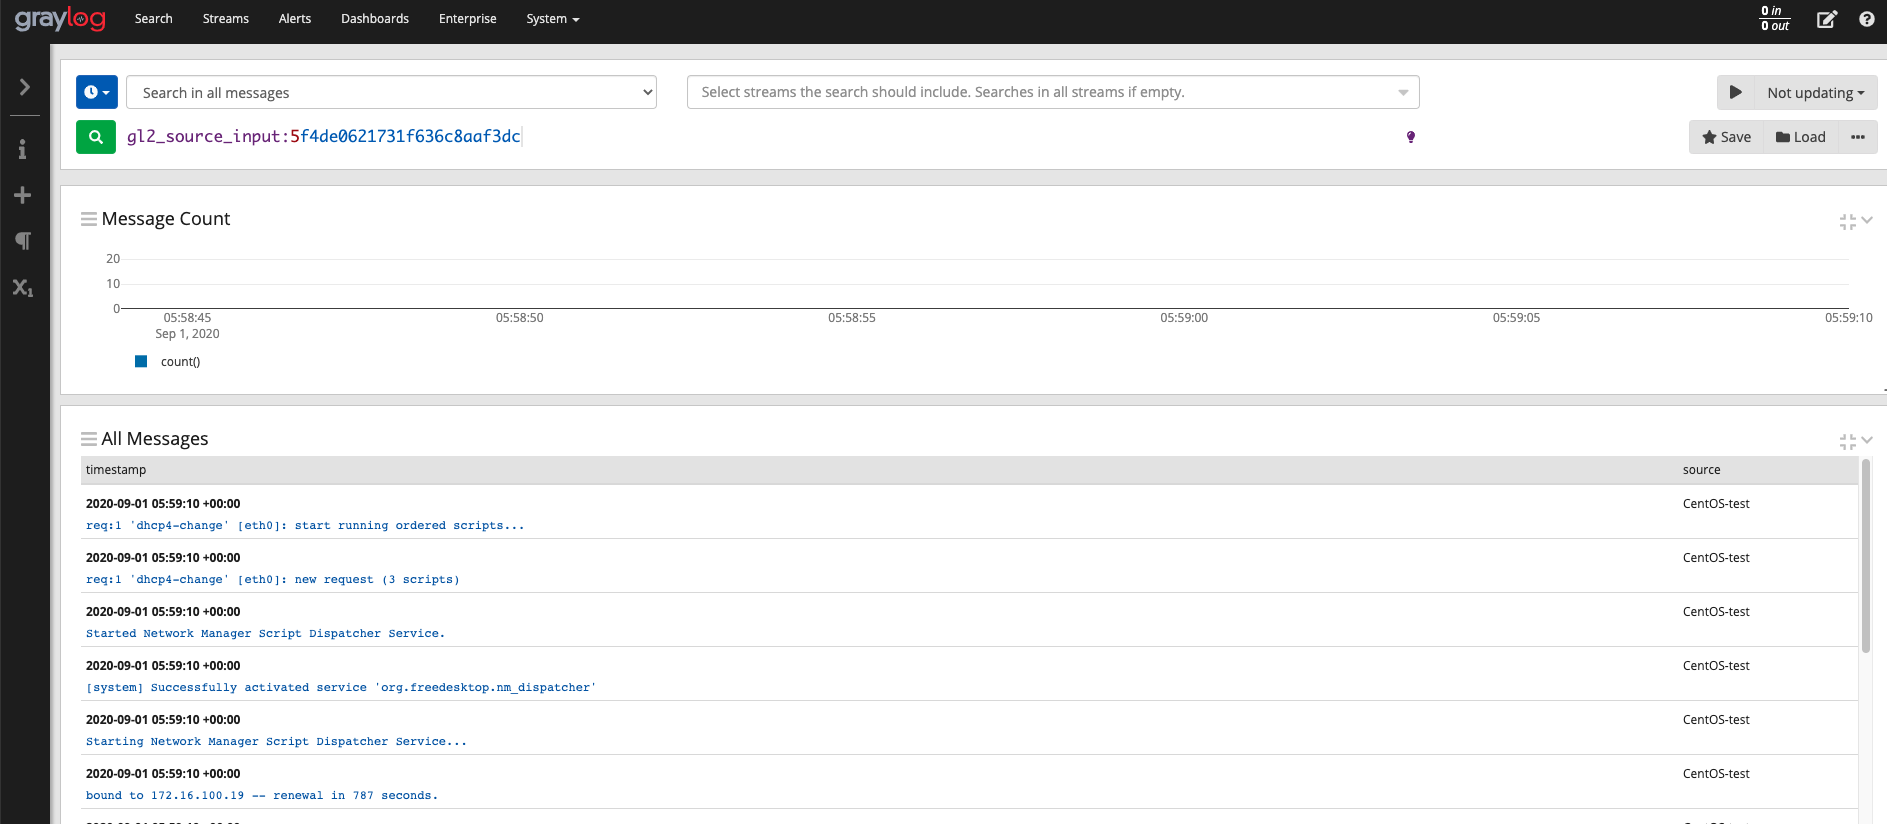
graylog日志系统接收rsyslog日志(二) Allen技术博客
Once you've uncommented the transport layer protocol and set a template, save your changes to.
使用rsyslog+loganalzey收集日志显示客户端ip图灵社区
Route, ospf, debug and raw. Many devices, especially routers and firewalls, do not send rfc.
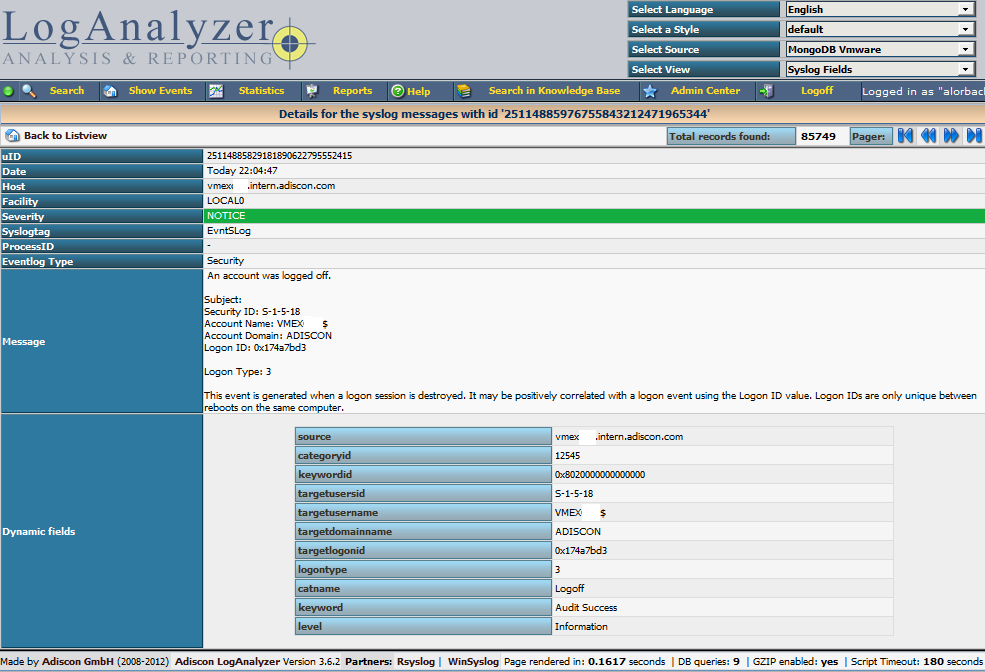
Using MongoDB with rsyslog and LogAnalyzer rsyslog
Rsyslog uses port 514 for network connectivity, whether it's using tcp or udp. Many devices,.

[SOLVED] [6.9.0beta25] through [6.9.0RC1] Syslog Server Broken, Error
There are many different template options available online. 随 rsyslog 版本不同,如果有如下警告信息,则将 ~ 修改为 stop。. Don't.

如何使用CentOS / RHEL中的Rsyslog创建集中式日志服务器7
You must deploy the aws cloudformation template in the aws account where you intend to.
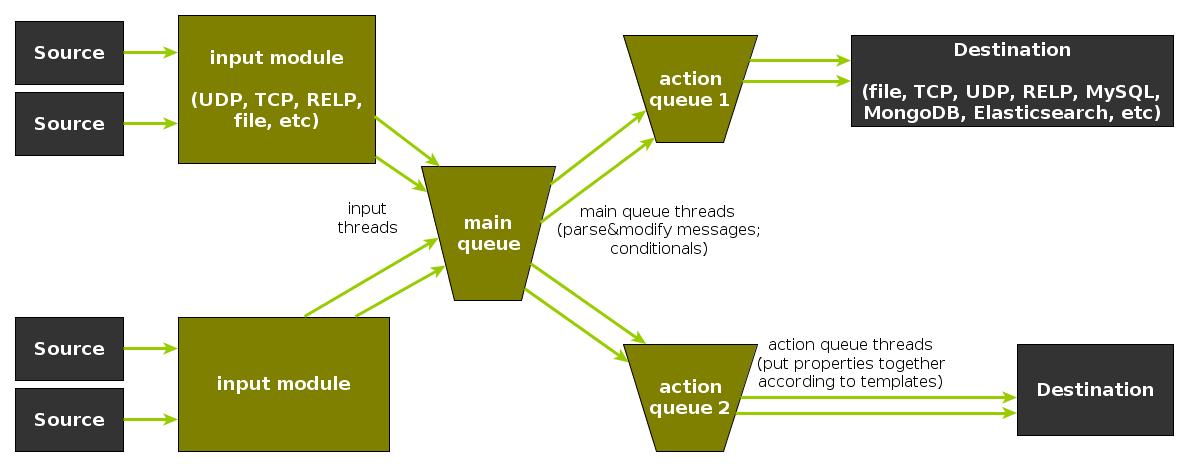
Rsyslog 8.1 Elasticsearch Output Performance Sematext
Graylog is able to accept and parse rfc 5424 and rfc 3164 compliant syslog messages.
随 rsyslog 版本不同,如果有如下警告信息,则将 ~ 修改为 stop。. You must deploy the aws cloudformation template in the aws account where you intend to store your log data. There are many different template options available online. # systemctl restart rsyslog firewall. Once you've uncommented the transport layer protocol and set a template, save your changes to the file. For example, ospf debug logs have four different topics: In the next step we need to create a template for remote messages, and tell rsyslog daemon how to record messages received from other client machines. Graylog is able to accept and parse rfc 5424 and rfc 3164 compliant syslog messages and supports tcp transport with both the octet counting or termination character methods. Start with a tailored template for your projects and tasks, and build the workflow and process you need with the tools at your fingertips. Each log entry have topic which describes the origin of log message. Clickup is the online solution to let your team get more done! Easily manage your team's tasks from anywhere in the modern world. Rsyslog uses port 514 for network connectivity, whether it's using tcp or udp. Log ingestion, log indexing, and visualization. Route, ospf, debug and raw.
In The Next Step We Need To Create A Template For Remote Messages, And Tell Rsyslog Daemon How To Record Messages Received From Other Client Machines.
Open /etc/rsyslog.conf with a text editor, and append the following template before the global directives block: You must deploy the aws cloudformation template in the aws account where you intend to store your log data. For example, ospf debug logs have four different topics: The centralized logging on aws solution contains the following components:
# Systemctl Restart Rsyslog Firewall.
Udp Is Also Supported And The Recommended Way To Send Log Messages In Most Architectures.
Don't forget to restart rsyslog. Rsyslog uses port 514 for network connectivity, whether it's using tcp or udp. Clickup is the online solution to let your team get more done! Create a template for log receipt.
Many Devices, Especially Routers And Firewalls, Do Not Send Rfc Compliant Syslog Messages.
There are many different template options available online. 随 rsyslog 版本不同,如果有如下警告信息,则将 ~ 修改为 stop。. Log ingestion, log indexing, and visualization. Amazon cloudwatch logs destinations deploy in the primary account and are created with the required permissions in.