Nist 800-171 Access Control Policy Template
Extensible access control markup language (xacml) and next generation access control (ngac). A comparison of attribute based access control (abac) standards for data service applications: Every element of an information security program (and every security control put in place by an entity) should be designed to achieve one or more of these principles. The exception is the parameters property that passes values from the policy to the template. The fundamental principles (tenets) of information security are confidentiality, integrity, and availability.
Nist 800-171 Access Control Policy Template - The exception is the parameters property that passes values from the policy to the template. Together, they are called the cia triad. February 2020 (includes updates as of january 28, 2021) supersedes: As components of the template, not the policy. Cmvp validation authority updates to iso/iec 24759 and. The fundamental principles (tenets) of information security are confidentiality, integrity, and availability. With aws, you control where your data is stored, who can access it, and what resources your organization is consuming at any given moment. Every element of an information security program (and every security control put in place by an entity) should be designed to achieve one or more of these principles. Extensible access control markup language (xacml) and next generation access control (ngac). A comparison of attribute based access control (abac) standards for data service applications:
Nist 800-171 Access Control Policy Template Gallery

Nist 800 171 Access Control Policy Template Templates MTAwNjkx
The exception is the parameters property that passes values from the policy to the template..
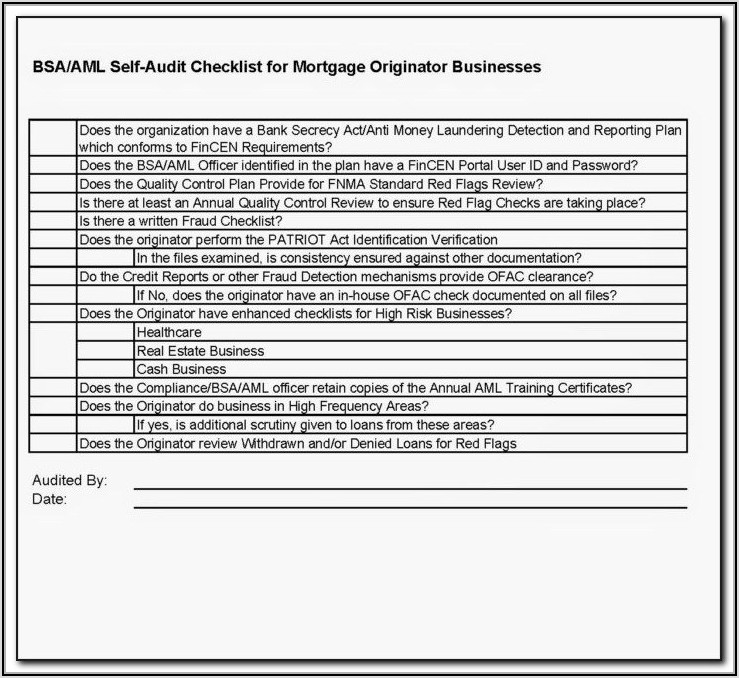
It Security Policy Template Nist Template 1 Resume Examples 7NYAXnb9pv
Cmvp validation authority updates to iso/iec 24759 and. A comparison of attribute based access control.

NIST Cyber Security Framework Security Line Card
Every element of an information security program (and every security control put in place by.
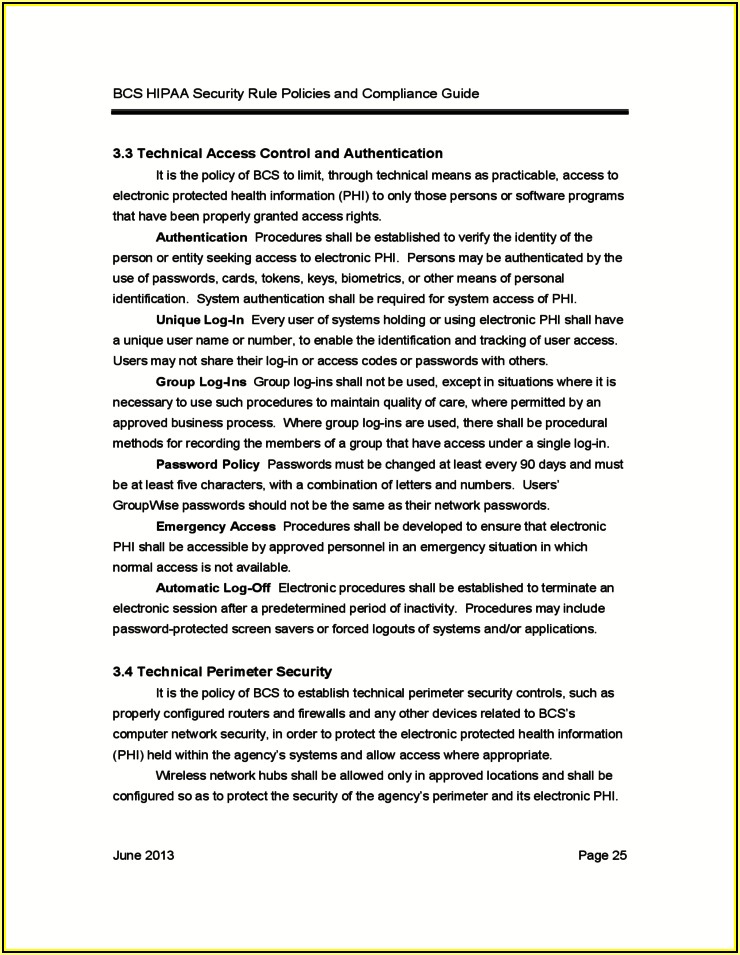
Information Security Policy Template Nist Template 1 Resume
Every element of an information security program (and every security control put in place by.

Nist 800 171 Poa&m Template Template 1 Resume Examples 05KAgna8wP
The exception is the parameters property that passes values from the policy to the template..
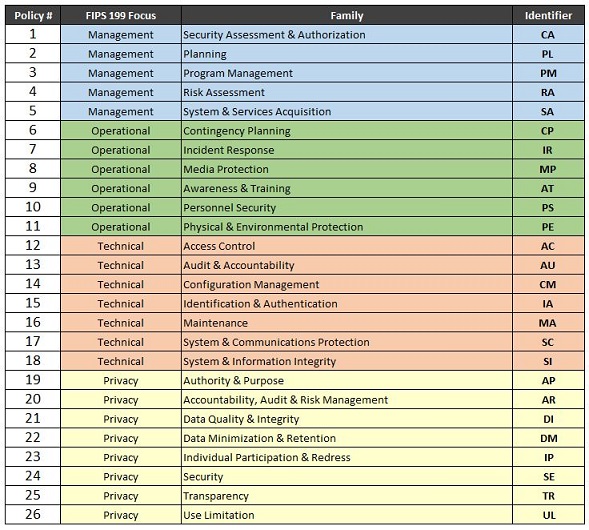
Nist Policy Templates
Cmvp validation authority updates to iso/iec 24759 and. Together, they are called the cia triad..
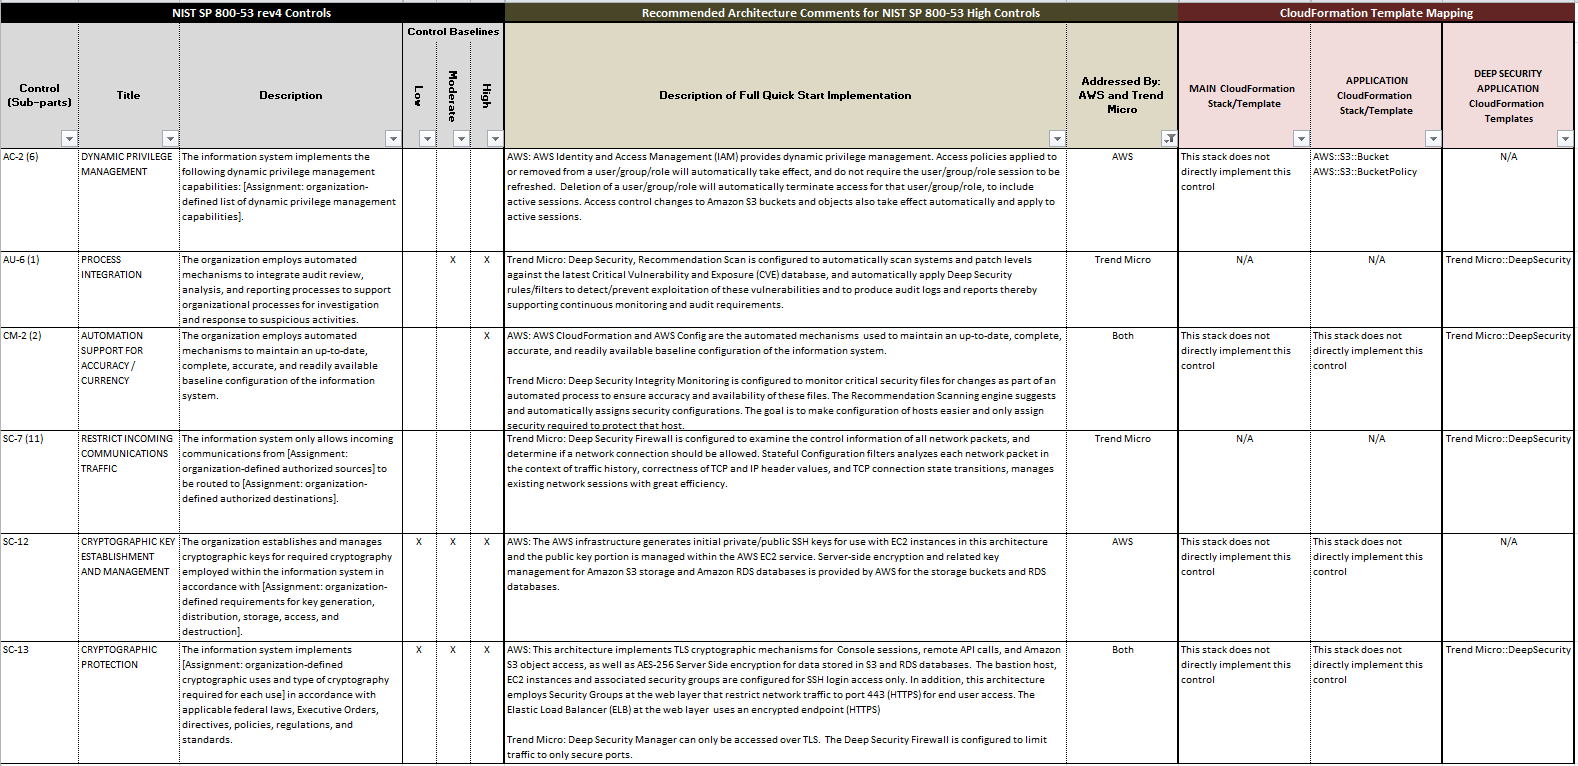
Nist Policy Templates
Extensible access control markup language (xacml) and next generation access control (ngac). Together, they are.
Nist 800 171 Access Control Policy Template Template 1 Resume
With aws, you control where your data is stored, who can access it, and what.
As components of the template, not the policy. Every element of an information security program (and every security control put in place by an entity) should be designed to achieve one or more of these principles. February 2020 (includes updates as of january 28, 2021) supersedes: The exception is the parameters property that passes values from the policy to the template. A comparison of attribute based access control (abac) standards for data service applications: Cmvp validation authority updates to iso/iec 24759 and. Together, they are called the cia triad. With aws, you control where your data is stored, who can access it, and what resources your organization is consuming at any given moment. The fundamental principles (tenets) of information security are confidentiality, integrity, and availability. Extensible access control markup language (xacml) and next generation access control (ngac).
Cmvp Validation Authority Updates To Iso/Iec 24759 And.
Every element of an information security program (and every security control put in place by an entity) should be designed to achieve one or more of these principles. Together, they are called the cia triad. As components of the template, not the policy. A comparison of attribute based access control (abac) standards for data service applications: